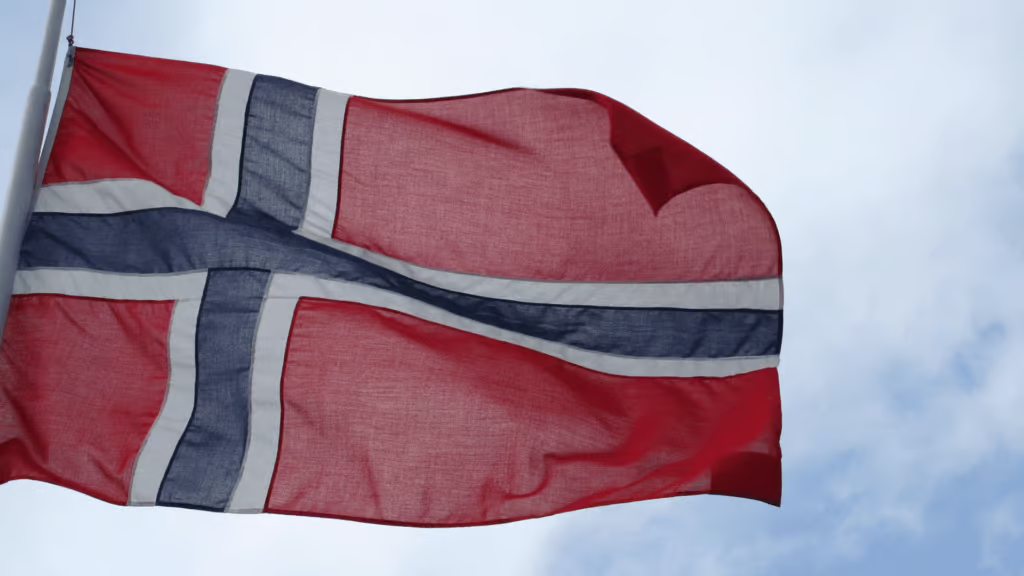
The Norwegian National Security Authority has issued warnings regarding heightened cybersecurity risk to the country’s critical infrastructure. The agency has also requested businesses take measures to strengthen their security.
In its first public assessment of the national cyber risk level, NSM warned on October 28 that the country’s defence, space, and other critical infrastructure sectors face “a high level of” cybersecurity risks. Attackers are continuously probing the country’s networks, mapping infrastructure, and installing ransomware, it added.
“We have seen a tripling of successful cyber operations against Norwegian businesses in the past half of the year. Several of these have had serious consequences,” said NSM Director Arne Christian Haugstøyl.
He added that the rapid escalation may also be caused by advances in AI, as they allow attackers to analyze large volumes of data and find vulnerabilities faster. “This means that the risk increases, and the pace of carrying out security measures needs to be up,” he added.
A string of Russia-linked attacks
The alert from the agency comes as the country continues to witness Russian espionage activities against Norway. The country is a key Ukrainian ally and leading gas pipeline supplier in Europe.
This week the Norwegian Prime Minister, Jonas Gahr Støre, alongside Finnish President, Alexander Stubb, held a three-way phone call with Vladimir Putin, with Stubb stating that an end to the Ukrainian conflict “will not be achieved through silence.”
Earlier this year, the pro-Russian group Server Killers claimed responsibility for a large-scale cyberattack against the Norwegian Digitalization Agency.
In 2025, the Norwegian Police Security Service attributed a disruptive cyberattack against control systems of the Risevatnet dam in western Norway to Russian hacktivist groups. The attackers took control of the facility and opened the water flow.
NSM has also urged organizations to deploy cyber hygiene practices to prevent potential compromises. These include companies mapping their supply chains, establishing appropriate monitoring, and ensuring proper implementation of security measures.
“NSM is aware that cyber operations also affect businesses that are subcontractors to businesses that have an impact on national security,” the agency said. “There may be attempts by the threat player [actor] to access other businesses higher up in a supplier or value chain.”