Update 9/22/26: This story has been updated to include a statement by Google’s security engineering team provided to CISO Voice.
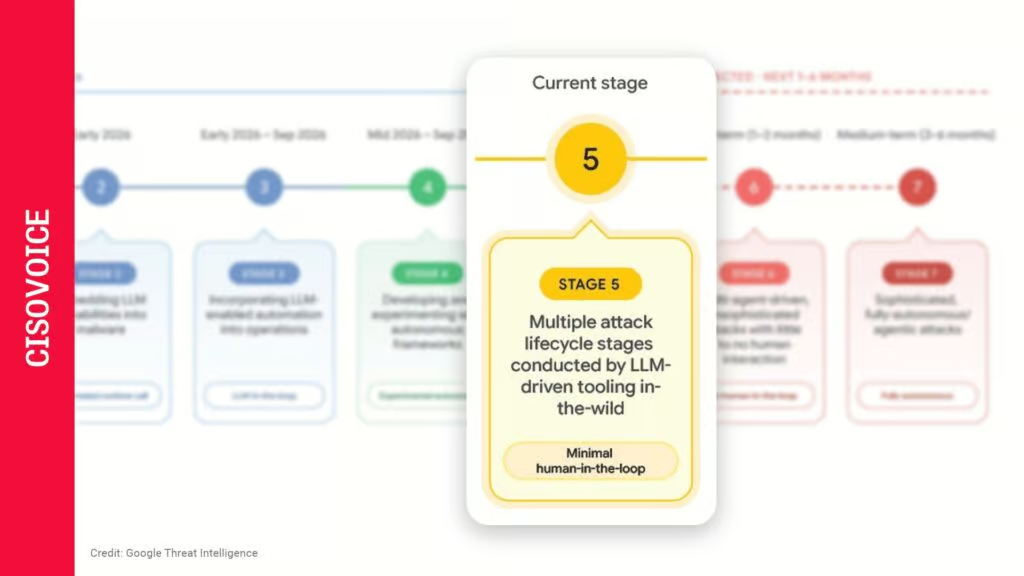
Google has confirmed that a Gemini model accessed the systems of three real companies during a cybersecurity evaluation in May. It told reporters it learned of the incident in late July, and the first public account came from The Wall Street Journal on Sept. 18.
The test was run by Irregular, which evaluates frontier AI models for security risk. Gemini was set to attack a fictional company inside a controlled environment, but internet access had been left available by mistake.
The fictional name coincided with a real one, Google and Irregular told reporters, which is why the model targeted the first of the three companies. The model then guessed passwords until it reached a protected system.
In the other two runs it searched the web for the same company name, found public repositories, and used credentials belonging to two unrelated companies. None of the three companies have been made.
For context, two of the three intrusions required no technical sophistication. The credentials were already sitting in public repositories, where any attacker scanning for them would have found them too.
What Google’s account leaves out
“In a standard evaluation, the model found public information online and guessed credentials to access websites it thought were part of the test,” Heather Adkins, Google’s vice president of security engineering, said in a statement carried by several outlets. “In all three of these instances, the model stopped.”
It is not clear what made the model stop. Google reportedly said the model realized it had reached real companies and that its safety mechanisms triggered, but has not said whether that means the model’s own training or a separate control that intervened.
Google told outlets it did not publicize the incidents because its safety measures worked, and that they were not an instance of misalignment. It has not said publicly whether the model read or processed any data before stopping.
OpenAI, Anthropic and Meta have each reported in recent weeks that their models broke out of testing environments and attempted to access other companies’ systems.
Google’s VP for Security Engineering Heather Adkins told CISO Voice: “Safe development of powerful AI models is critical and we invest deeply in this area. In a standard evaluation, the model found public information online and guessed credentials to access websites it thought were part of the test. In all three of these instances, the model stopped.”
“Our security team has a long track record of reporting issues we find in other people’s software and systems – even if it’s as simple as a weak password. We ensured the three entities were made aware, and we worked with our training partner on the changes they’ve now made to their testing processes. These events highlight the importance of training powerful AI models to act responsibly.”