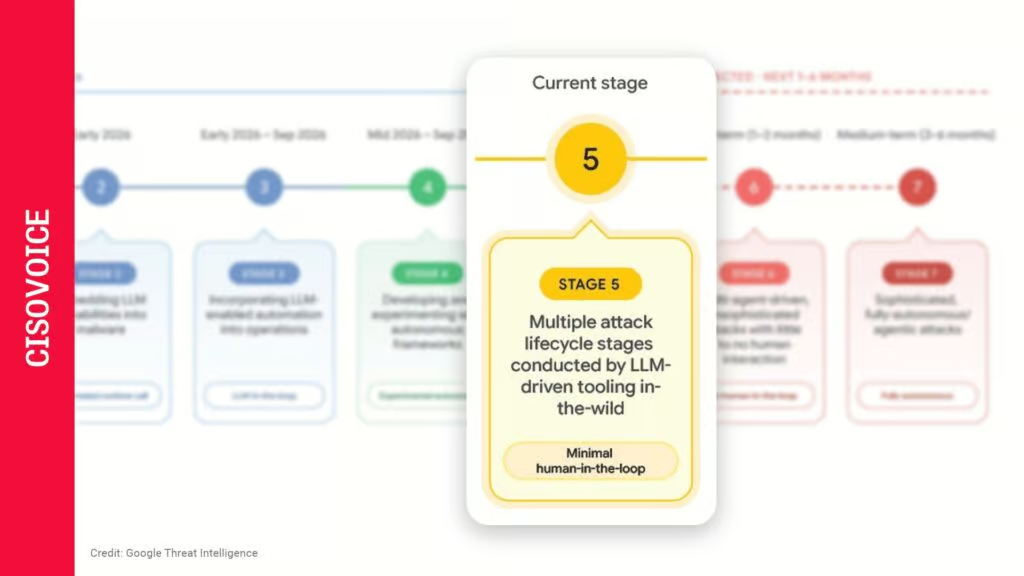
A Chinese-speaking threat actor deployed multiple AI models in a hacking campaign to scan for vulnerable devices and identify exploits for the identified flaws. The hacking campaign attempted to compromise nearly 500 systems, security firm Palo Alto Networks said.
Palo Alto’s Unit 42 attributed the campaign to a Chinese-speaking threat actor who goes by the aliases knaithe and KnYuan. The hackers, who ran the operation via Telegram, seemingly used the Hermes Agent framework as their autonomous offensive operator, which they combined with DeepSeek for its reasoning capabilities.
The attackers also configured multiple large language models, including Qwen, GLM, Kimi and MiniMax, as well as probing Claude Code for connectivity testing and proxy validation. The attackers also seemingly used the AI software engineering agent Codex for scanning the exploit development directory.
“From our analysis and visibility, we identified that this actor attempted to exploit over 460 targets, leveraging a mix of autonomous and manual techniques. What’s interesting is that the actor appeared to allow DeepSeek to narrow the targeting scope, likely to conserve AI compute,” Palo Alto said..
The hackers used the tactics to mainly target victims in China, Malaysia and another unidentified country. “The actor’s broader activity is opportunistic,” the report continued.
In the campaign, the hackers deployed the Hermes agent as the primary offensive AI tool for tasks such as LLM jailbreaking, framework bundling, unauthenticated WebSocket exploitation and for probing FOFA, a cyberspace search engine used to identify internet-connected devices, servers and public network assets.
The attackers then combined the Hermes agent with DeepSeek, which served as the reasoning engine for code generation, vulnerability assessment, target selection and decision-making. The report, however, did not specify which DeepSeek model the threat actors used. Palo Alto did not immediately respond to a request for comment.
Although the Hermes agent scanned for a Langflow vulnerability tracked as CVE-2026-33017 downloaded a public proof-of-concept exploit, as well as enumerated 84 Langflow instances, the operation failed due to security configurations on the targeted system.
The AI system then abandoned the operation and scanned FOFA to find systems vulnerable to more critical flaws, and then probed GitHub for trending 2026 CVE proof-of-concept repositories to exploit the identified flaws.
In the next stage, the DeepSeek model obtained exploits for two vulnerabilities to target Chinese systems running on the AI workflow automation application n8n. These flaws included CVE-2026-21858 and CVE-2025-68613.
“DeepSeek launched parallel scanning across 50-plus remaining Chinese targets. None had publicly accessible forms. The actor did not achieve exploitation,” Palo Alto researchers said.
Additionally, the hackers conducted manual operations to exploit vulnerabilities affecting Citrix NetScaler, Marimo notebook instances, Apache Tomcat servers and IKE VPN endpoints.
AI Concerns
Though the campaign did not result in a full compromise, Palo Alto said it demonstrates that threat actors are “constructing persistent AI offensive infrastructure” by combining automated and manual operations.
The actor routed Claude Code and Codex through an anonymising proxy and still moved to DeepSeek, because provider-side controls limited the Western models. OpenAI confirmed to Unit 42 that its safeguards refused the requests and that it disabled a linked account
“The actor is actively iterating — refining tool configurations, developing custom skills, establishing proxy infrastructure and executing autonomous attack cycles. The technical barrier to AI-augmented offensive operations is low and continues to decrease,” Palo Alto added.
The campaign also marks the latest instance of threat actors using the Hermes AI agent to target victims. Last week, another suspected Chinese hacking group used Hermes to probe vulnerabilities, enumerate hosts and search files.
Prior to that, OpenAI claimed its GPT-5.6 Sol model and an unreleased model compromised Hugging Face, adding to ongoing concerns about AI models’ disruptive capabilities.