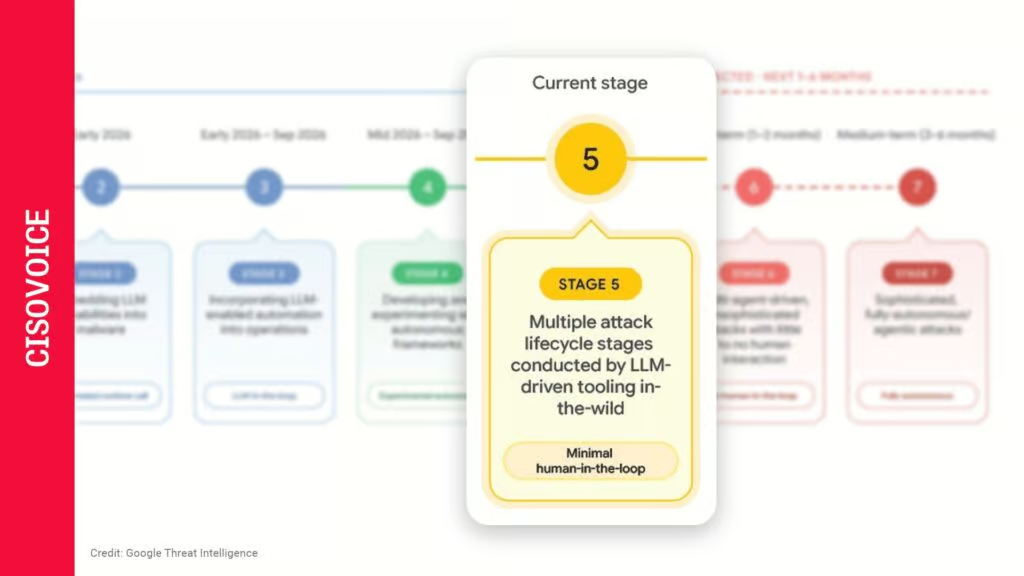
Threat actors have used large language model (LLM) frameworks to fully automate vulnerability discovery and exploitation without a human in the loop for the first time, Google Threat Intelligence Group (GTIG) said in a report published Nov. 16.
GTIG found an exposed staging server hosting a multi-agent framework it called “exploit_agent.” Integrated with multiple frontier and local LLMs, it continuously compared popular web application software before and after patch announcements, identified potential vulnerabilities, drafted exploits and executed them automatically.
The server also contained stolen victim data and scripts for post-compromise activity. Telemetry suggested the operator targeted French websites in media, entertainment and education.
GTIG said attackers may find it more efficient to use LLMs on patched “n-day” flaws, because they can focus on a limited set of material, such as code versions, release notes and proof-of-concept (PoC) code. It said this was shrinking the window organizations had to patch before attacks began.
LLMs are accelerating exploitation and multi-stage intrusions
In late August, attackers exploited two chained PaperCut vulnerabilities as zero-days. GTIG said researchers and Huntress used LLMs to generate working exploits within a day of disclosure. It also cited GreyNoise reporting a campaign four days after disclosure in which an attacker likely used LLMs to develop and test exploits before targeting hundreds of organizations. In one case, it expanded a foothold to domain administrator within minutes.
GTIG also found attackers using open-source multi-agent frameworks including ARTEX, CAIRN, CyberStrikeAI and PentAGI.
It observed CAIRN used against targets including the US aerospace sector, and linked framework experimentation to financially motivated actors and suspected PRC-nexus espionage groups. GTIG said these tools currently “trade stealth for velocity,” leaving traces that increase the likelihood of detection.
“These attacks still rely on familiar methods like compromised credentials and unpatched systems,” Sally Vincent, senior threat research engineer at Exabeam, told CISO Voice. “AI helps attackers carry out that work faster and with less human involvement.”
She said behavioral detection could flag unfamiliar tool use, unusual data access or changes in activity volume, “even when the attacker uses legitimate tools and valid credentials.”
Mandiant also responded to LLMJacking incidents in 2026, in which attackers stole LLM credentials and cloud resources. In some cases, single-day fraudulent charges exceeded $100,000, and in the most severe, cumulative abuse reached $1 million before remediation.