Phishing activity in Europe has surged 4.5 times year over year, against a 1.5 times increase worldwide, according to research published today.
European users also clicked more often. Proofpoint found 8.3 clicks for every 100 delivered threat messages in Europe, compared with 2.0 worldwide.
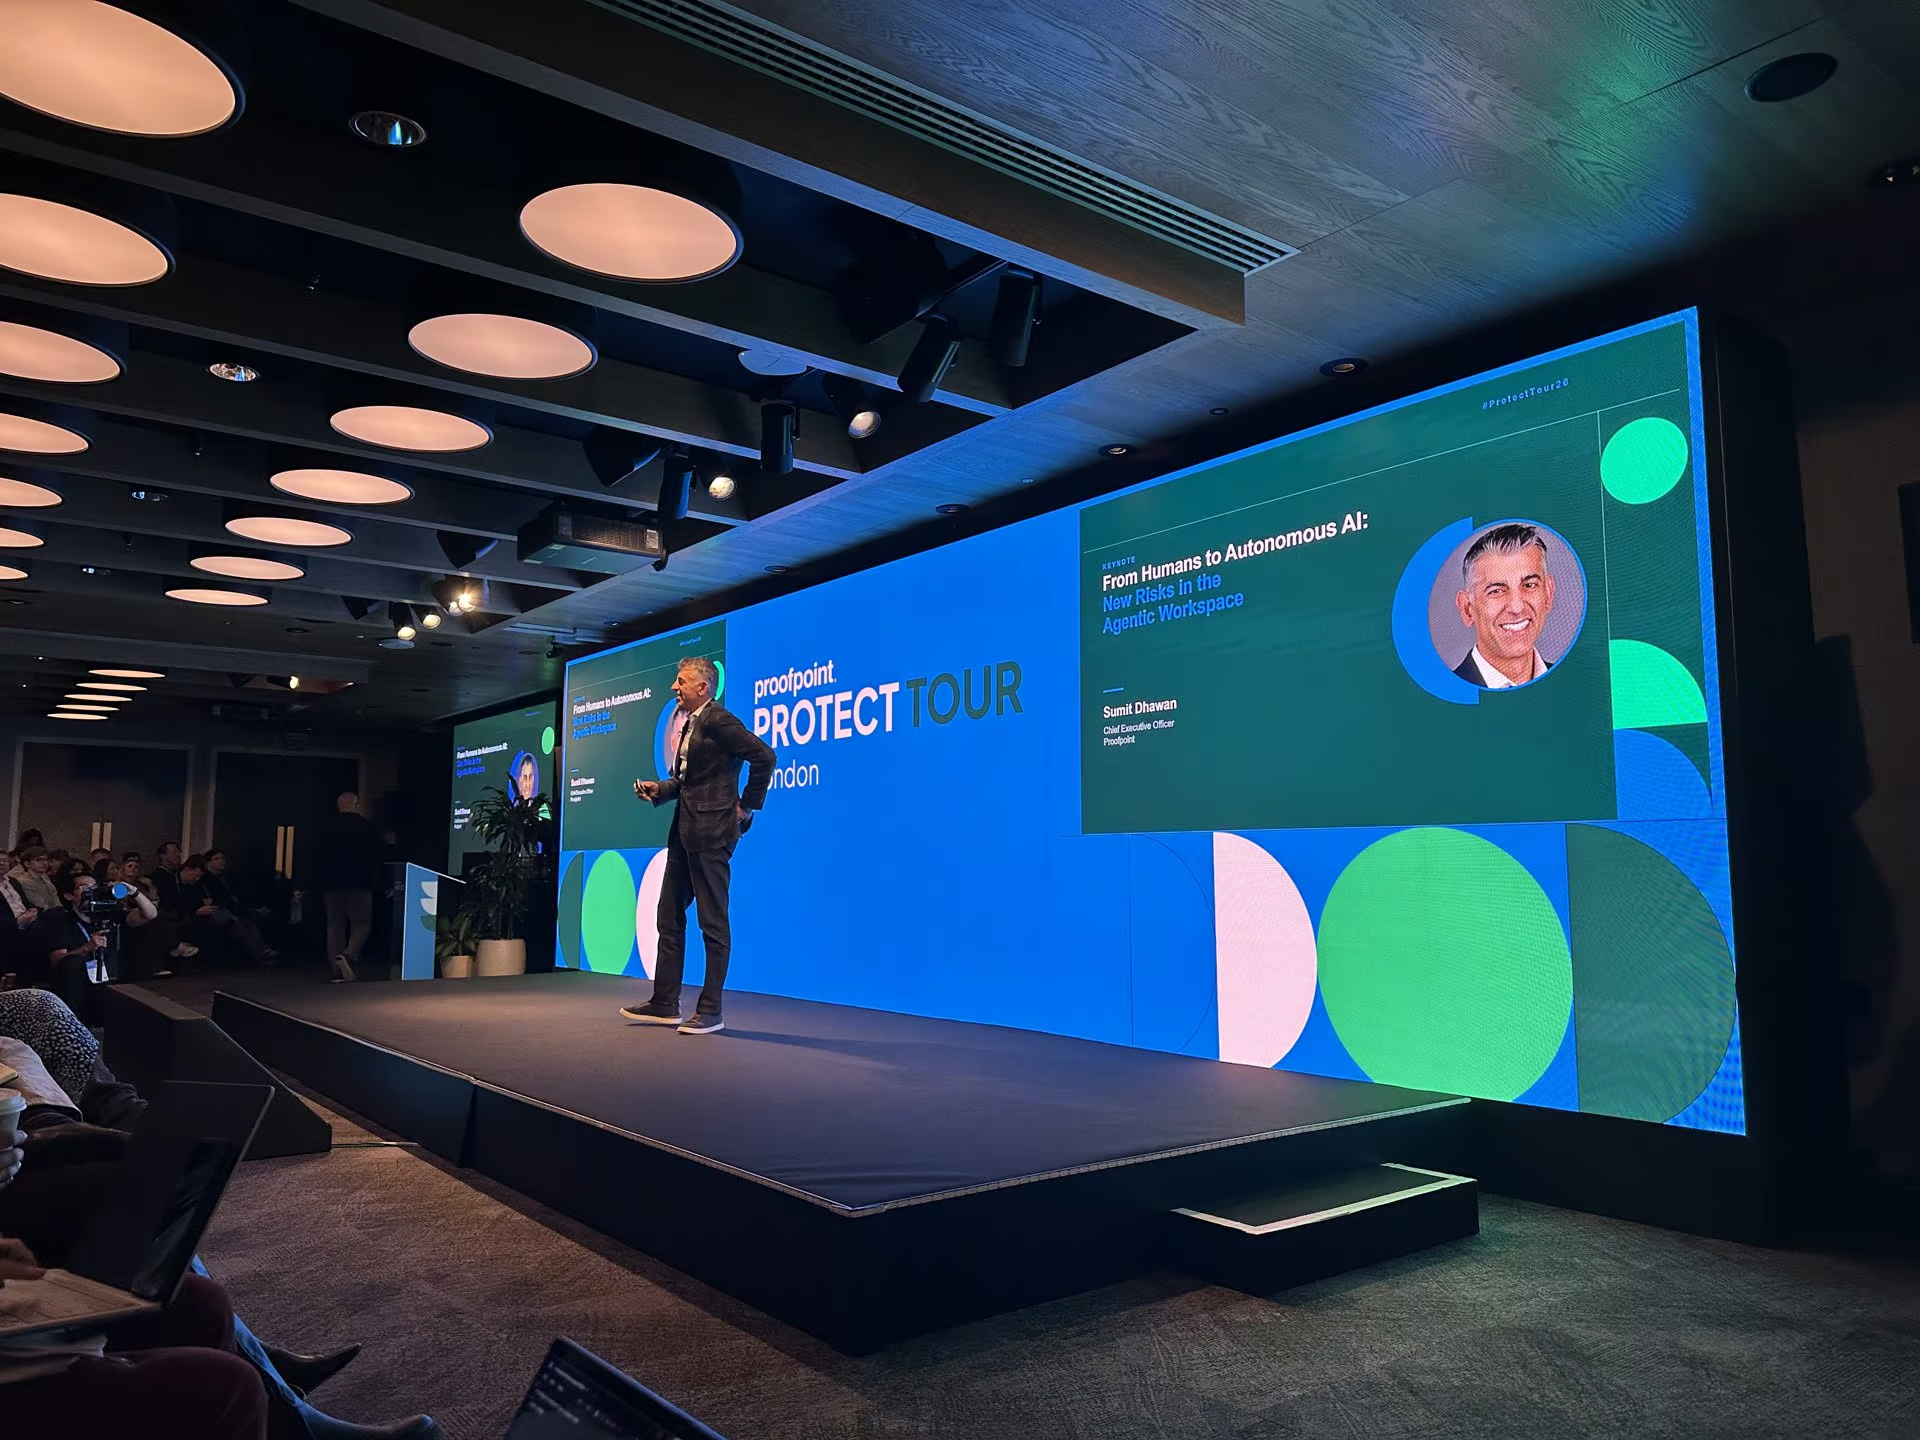
Speaking to CISO Voice at Proofpoint Protect Tour London today, Proofpoint CEO Sumit Dhawan said growth in the UK was higher still. “It’s even higher in the UK, which is actually more surprising to me,” he said. Dhawan said AI is making language less of a barrier for attackers targeting the rest of Europe, but that barrier never applied to English-speaking UK targets.
AI is speeding attackers up
Proofpoint’s report said state-aligned groups are using large language models (LLMs) to build tools faster. Proofpoint assessed that LLMs have “very likely accelerated” custom malware and phishing kit development by TA395, a South Asian group expanding into Western Europe.
It also said LLM-assisted research has accelerated exploit discovery by TA488, a Russian group that targets Outlook, Zimbra and other webmail.
Daniel Blackford, VP of threat research at Proofpoint, said threat actors across most of the landscape, not only nation-state groups, have adopted AI coding assistants in the last six to eight months.
More advanced groups use AI to act faster once inside a network. Blackford pointed to Proofpoint research on a password-spraying campaign against Chilean organizations, including a major retailer. Seven Microsoft 365 accounts were compromised, and in one case the attacker began post-access activity within 90 seconds.
He said the same groups are now pivoting to the UK, using AI to scale and to write in the local language. Defenders have kept ahead of attackers’ use of AI so far, he said, but the window for defenders “is rapidly collapsing.”
In the cloud, the report found that, of European organizations targeted by precision cloud attacks, 64% showed evidence of impact, against 33% for brute-force attacks. Blackford said precision attacks suggest the attacker already holds valid credentials, often from an earlier phishing attack.
“Good enough” is no longer enough for SMBs
Dhawan said many European organizations, particularly mid-market and smaller firms, have for too long relied on basic protection. He said that is no longer a viable strategy.
“You need the most sophisticated protection, regardless of who you are and what size customer you are,” Dhawan said. He added that Europe has a larger share of smaller enterprises than the US, so a higher share of attacks landing in Europe did not surprise him.
Blackford said only a small share of Proofpoint’s customers see nation-state espionage, but some of those are small and medium businesses. He said attackers see smaller firms as “a softer target” and a direct route into the larger organizations they supply.