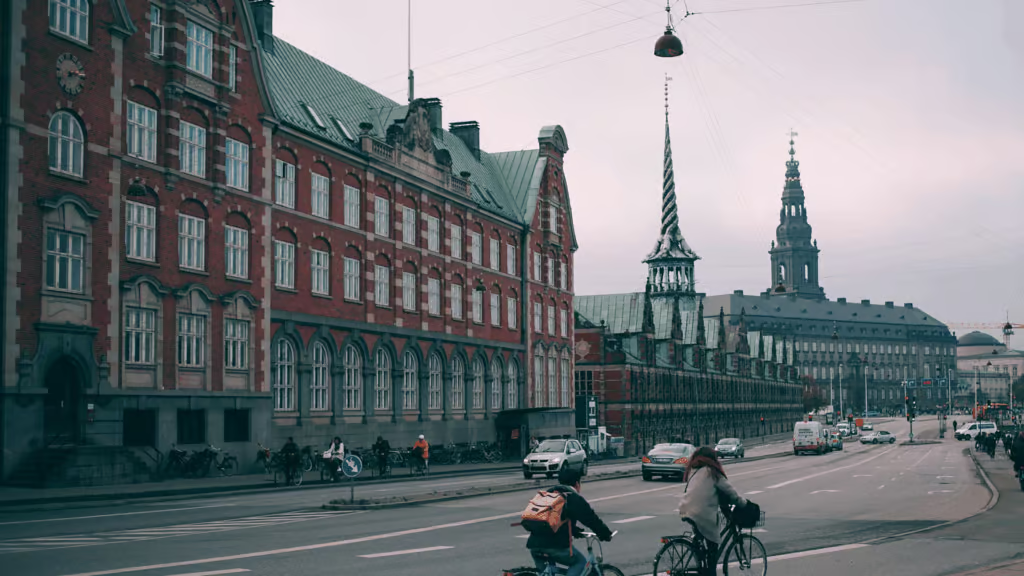
Hackers breached the University of Copenhagen to access names, national identity numbers, and contact details of about 525,000 individuals, as well as ID card PIN codes.
The university said it detected the breach on Tuesday, Oct. 20, after hackers gained access to one of its test environments, and disclosed it on Oct. 23.
On Monday, it said it had been exposed to a new attack and shut down some administrative systems, but earlier today it corrected this, saying the activity was not a new attack.
“There are operational disruptions on several administrative systems, e.g. Workzone and Nimbus,” it said in an update on Monday. “This is a preventive and controlled shutdown of the administrative systems in question.”
The university said the shutdown remains linked to the original cyberattack, and that some of its systems continue to experience disruptions.
What the hackers accessed
In the initial compromise, the unidentified attackers accessed information of nearly 525,000 individuals. These included names, national identity numbers, work telephone numbers, home telephone numbers, and personal email addresses. The attackers also accessed the PIN codes of about 20,000 staff and students’ ID cards, which have since been replaced.
“Access has been blocked, and the university is working intensively to establish the full extent of the incident and to prevent similar or further attacks from taking place,” the university added. It said there is no indication the hackers gained access to systems supporting day-to-day operations.
The university has further notified the Danish Data Protection Agency, as it considers the incident to fall within the scope of the General Data Protection Regulation, and said other relevant authorities are kept closely informed.
The data regulator did not immediately respond to a request for comment.
It is the second large exposure of Danish national identity numbers this month, after a breach that exposed the data of 8.8 million people was disclosed on Oct. 5.